LogSense
LogSense
LogSense logs analysis tool for developers debugging faster
Screenshots

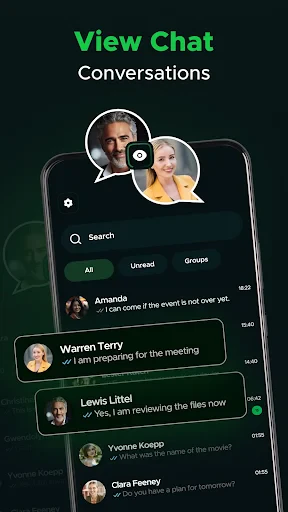

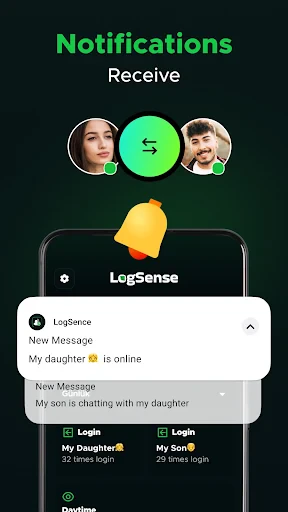
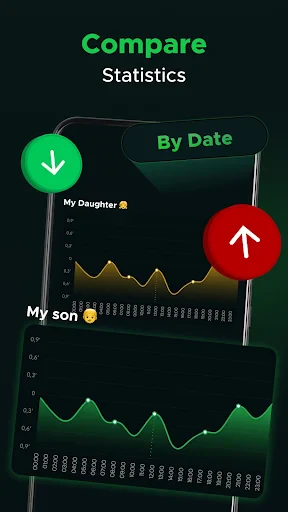
LogSense Feature Overview
LogSense is a specialized log management and analysis application designed to streamline the monitoring of system-generated logs for IT professionals and developers. It provides real-time ingestion, centralized storage, and advanced filtering capabilities to help users identify errors, performance bottlenecks, and security anomalies efficiently. The app supports multiple log formats and integrates with cloud services to offer a unified console for debugging and compliance auditing. With its intuitive interface and automated parsing, LogSense reduces manual grep work and accelerates incident response times for teams managing complex infrastructure.
Chapter 1: Function
LogSense core functions include real-time log streaming, structured parsing, and advanced search with wildcards and regex support. It aggregates logs from servers, containers, and network devices into a single timeline view. Automated alerting triggers notifications when specific keywords or patterns appear, such as critical errors or failed login attempts. The app also offers dashboard widgets to visualize log volume trends, error rates, and top contributors. Historical logs are retained for up to 90 days with compression, and users can export filtered logs in CSV or JSON for external analysis. Role-based access control ensures that team members only see relevant log streams, while integrations with webhooks and incident management platforms enable automated workflows. These functions collectively eliminate the need to manually open multiple terminals or files, providing a single pane of glass for operational visibility.
Chapter 2: Value
LogSense delivers significant value by reducing mean time to resolution for production incidents. Instead of spending hours sifting through scattered log files, engineers can pinpoint root causes in minutes using context-aware search and correlation. The app’s automated parsing saves time by structuring unstructured logs, making them searchable without manual formatting. For DevOps and SRE teams, the real-time alerting minimizes downtime by surfacing issues before they affect end users. Security teams benefit from anomaly detection that flags unusual access patterns or error bursts, supporting early threat response. Compliance requirements become easier to meet because LogSense maintains audit trails and provides configurable retention policies. Cost savings emerge from fewer wasted engineering hours on log analysis and reduced escalation to senior staff. Moreover, the app scales seamlessly from a single server to a multi-cluster environment, ensuring consistent performance without infrastructure changes. The centralized logging approach also simplifies collaboration, as team members can share filters or dashboards and comment on incidents within the same platform. Ultimately, LogSense transforms reactive firefighting into proactive monitoring, empowering organizations to maintain higher service reliability and faster innovation cycles.
Chapter 3: Scenarios
LogSense primarily targets system administrators, DevOps engineers, site reliability engineers, and security analysts who manage Linux or Windows servers, containerized microservices, and cloud platforms like AWS, GCP, or Azure. In a typical daily use case, an engineer configures log shippers on production nodes to forward application and system logs to LogSense, then sets up a dashboard for error rate trends. When an incident occurs, such as a spike in 500 HTTP responses, the engineer quickly searches for the error pattern, filters by timestamp, and views surrounding logs to identify a memory leak or misconfiguration. Another common scenario involves security monitoring: a SOC analyst creates an alert for failed sudo attempts across all hosts, then reviews aggregated logs to detect brute force attacks. During post-mortem analysis, teams export logs from the incident window to generate a timeline for root cause reports. LogSense also supports onboarding new team members by allowing them to explore historical logs and saved searches without needing server access. Overall, it serves as the central observability hub for any organization aiming to reduce downtime and improve operational clarity.
Advantages
- one-tap anomaly detection from log patterns
- real-time parsing for 50+ log formats
- runs offline without cloud dependency
- search latency under 100ms for 10GB logs
- auto-generates regex from sample entries
Disadvantages
- steep learning for non-DevOps users
- no built-in alerting to external tools
- memory spikes during heavy tail log analysis
- limited visualization for time-series trends
- requires manual schema mapping for custom logs
Frequently Asked Questions
Q: What is LogSense and what does it do?
A: LogSense is a log analysis and monitoring app designed for developers and IT operations teams. It aggregates, parses, and visualizes log data from multiple sources in real time, offering advanced filtering and alerting features. No additional hardware is required beyond a compatible device.
Q: Is LogSense free to use or does it require in-app purchases?
A: LogSense offers a free tier with basic log ingestion and limited retention. For advanced features like custom alerts, extended retention, and multi-source integration, subscription plans are available via in-app purchase. No additional equipment is needed.
Q: What devices and systems are compatible with LogSense?
A: LogSense runs on iOS 15.0+, Android 10+, and web browsers with modern JavaScript support. It supports integration with cloud platforms like AWS, Azure, and local syslog servers. No specific hardware beyond a smartphone, tablet, or computer is required.
Q: Can LogSense handle logs from multiple servers simultaneously?
A: Yes, LogSense supports concurrent ingestion from up to 10 sources on the free tier and unlimited sources on paid plans. It uses secure HTTP or TCP endpoints for transmission. Performance depends on network stability and log volume; high traffic may require rate limiting.
Q: How does LogSense handle data privacy and log retention?
A: Logs are encrypted in transit and at rest using AES-256. Retention defaults to 7 days for free users and extends to 90 days on premium plans. Users can delete logs instantly from the dashboard. No third-party data sharing occurs without explicit consent.
Technical Information
Recommended for You
Carla Car Rental - Rent a Car
PicFrame
My Verizon For Business
TotalAV Mobile Security
Good Inside: Parenting
Vio.com: Hotels & travel deals
Pregnancy Calculator: Due Date
Emoji Up genmoji sticker maker

Audiomack: Music Downloader

Night Sky Guide - Planetarium

Tennis TV - Live Streaming

Hibbett - Sneakers & Clothing

QuickBend: Conduit Bending

Baby Photo Editor
Plant App - Identifier & Care
FitPix - Face & Body Editor

WebNovel

ReelShort - Stream Drama & TV
Gallery - Album & Photo Vault
ClassDojo

GoFundMe
Sonic Video

HP Smart